

The nc command in Linux: Using it for network connections
Introduction
In the world of Linux administration, netcat (nc) is often called the "Swiss army knife" for working with networks. This compact but powerful utility handles sending and receiving data over the TCP and UDP protocols. Although netcat's functionality may seem limited, the tool copes perfectly with the tasks of testing connections, debugging network services and basic network communication.
What does the command give you?
Netcat is a universal network tool that finds a use in various system administration and development scenarios. Here are the utility's key capabilities:
- Working with TCP/UDP: Creating and managing connections over both protocols to test network services.
- Monitoring ports: The ability to listen on specific ports to analyse incoming connections.
- Transferring data: Setting up direct transfer of information between systems over a network.
- Chat functionality: Implementing a simple system for exchanging text messages between hosts.
- Port scanning: Discovering open network services on remote systems.
- Tunnelling: Redirecting network traffic through alternative ports or hosts.
- Proxy capabilities: Basic operation through proxy servers for network operations.
- Test web server: Quickly creating simple HTTP endpoints for testing.
The main command options
To work effectively with netcat, it's important to understand the key command-line options:
-6: Enable IPv6 support (by default -4 is used for IPv4)-h: Print help information about the available options-i: Set the delay interval between operations (in seconds)-l: Enable port listening mode-N: Automatically close the connection after a file transfer-n: Disable DNS resolving to work directly with IP addresses-P user_name: Specify the user for the proxy connection-x address:port: Set the proxy address and port-p port: Explicitly specify the port (usually determined automatically)-U: Use UNIX sockets for inter-process communication-u: Switch to the UDP protocol instead of TCP-v: Enable verbose output mode-w: Set the connection timeout in seconds-z: Scan without transferring data
Checking ports
One of netcat's main tasks – diagnosing the availability of network services. To check, use the combination of the -vz options:
$ nc -vz 192.168.31.247 8080

$ nc -vz 192.168.31.247 1-1000 2>&1 | grep succeeded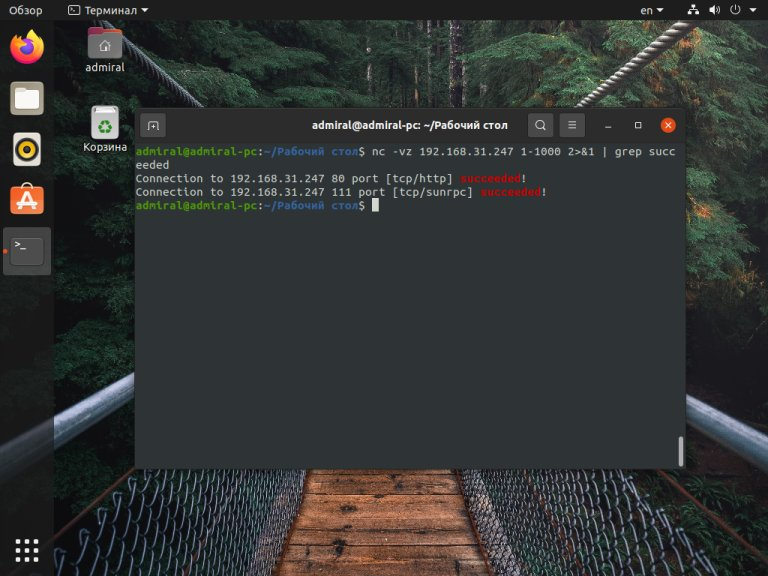
Screenshot with an example of running the command
To check UDP ports, add the -u option:
$ nc -vzu 192.168.31.247 1-1000 2>&1 | grep succeededIt's important to remember that UDP ports are always shown as available because of the specifics of the protocol.
Listening on ports
To monitor network activity, use listening mode:
$ nc -nlv 8080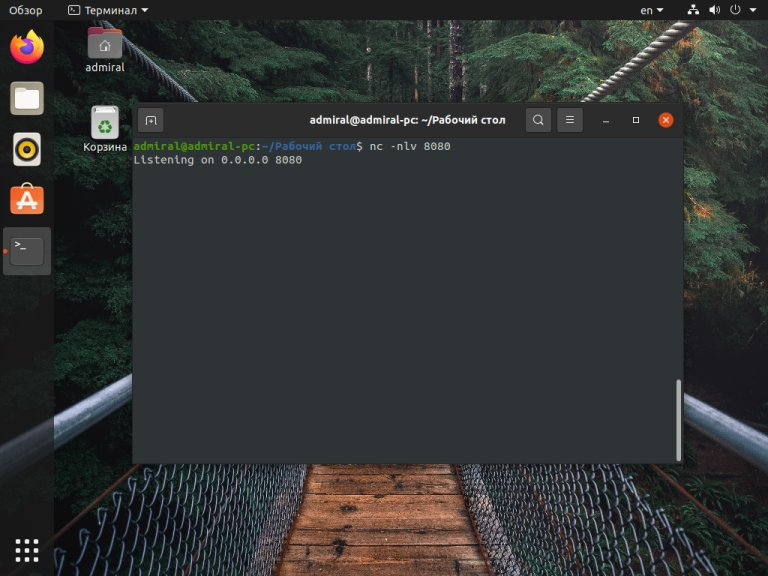
Screenshot with an example of listening on a port
WARNING
When using TCP, make sure the port is free – otherwise you'll get the "Already in use" error. Also remember that low ports (< 1024) require root privileges.
Transferring files
Netcat lets you set up a simple exchange of data between systems. Let's start with a basic example – a text chat.
On the receiving side:
$ nc -lp 8080
On the sending side:
$ nc 0.0.0.0 8080For transferring files the mechanism is similar. On the receiving side:
$ nc -l 8080 > paste.txtOn the sending side:
$ nc -N 0.0.0.0 8080 < copy.txtA simple web server
Netcat can be used to create a basic HTTP server. Although the functionality is limited, this is useful for quick testing:
$ while true; do echo -e "HTTP/1.1 200 OK\n\n$(cat index.html)" | nc -l -w 1 8080; done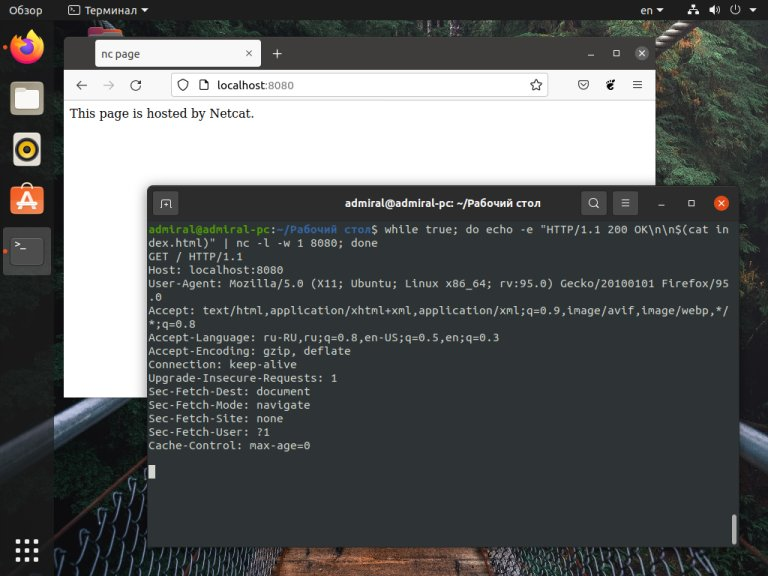
The -w 1 option ensures the connection is closed automatically if the browser doesn't do it.
Remote shell
Netcat can also be used for remote access to a system. Although the old -e option was removed for security reasons, there are alternative methods:
On the receiving side:
$ nc -lvnp 8080On the sending side:
$ rm /tmp/f; mkfifo /tmp/f; cat /tmp/f | sh -i 2>&1 | nc 0.0.0.0 8080 >/tmp/f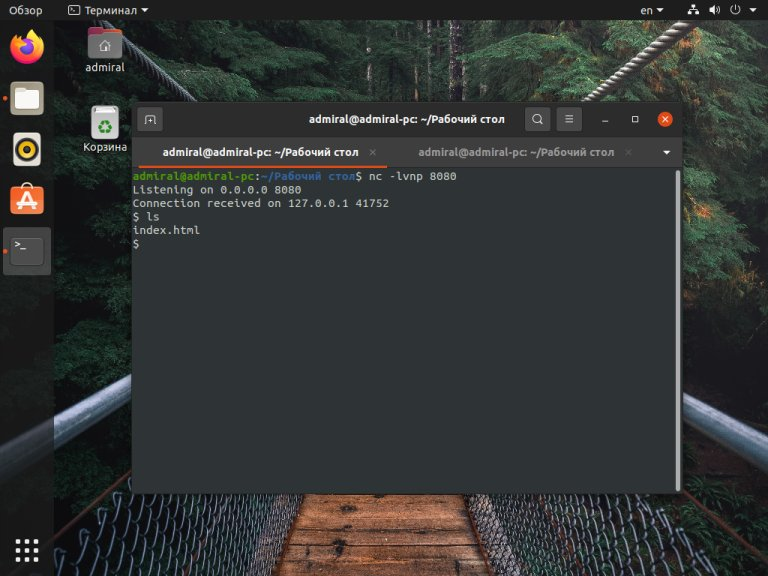
DANGER
Be careful with remote access – it's a potential attack vector. Always set up a firewall and follow security principles.
Additional resources
To get complete information about netcat's capabilities, use:
man ncINFO
Remember about security when working with network tools. Document all changes and regularly review your network protection settings.
Our resources
Telegram channel: https://t.me/
F3 Cloud: https://f3cloud.com